-
Using SS tool for network troubleshooting » IT Tips and Tricks
November 7, 2016 - permalink - https://tipstricks.itmatrix.eu/using-ss-tool-for-network-troubleshooting/Keepalive Notes
A keepalive packet generally has a TCP ACK configured with a sequence number set to one less than the current number used on the connection. Any machine receiving a nudge from such a packet will simply respond with the correct sequence number and, Frankenstein jokes aside, announce that it is indeed alive.
These types of packets are sometimes empty and generally have three associated parameters. The retry parameter will declare how many times to send a packet before coming to the conclusion that the other end of the connection has given up the ghost. The time setting is configured as the frequency of the checks, and finally the interval dictates the length of time between two sent packets if no response is received.
Inside the kernel, you can alter these settings by editing these values in the eye-watering pseudo-filesystem known and loved as /proc. One file, in this case, is /proc/sys/net/ipv4/tcp_keepalive_time, and you can edit it
-
-
What are useful command-line network monitors on Linux - Xmodulo
January 10, 2015 - permalink - http://xmodulo.com/useful-command-line-network-monitors-linux.htmlplein d'outils network linux
+ nloadvia arnaub
-
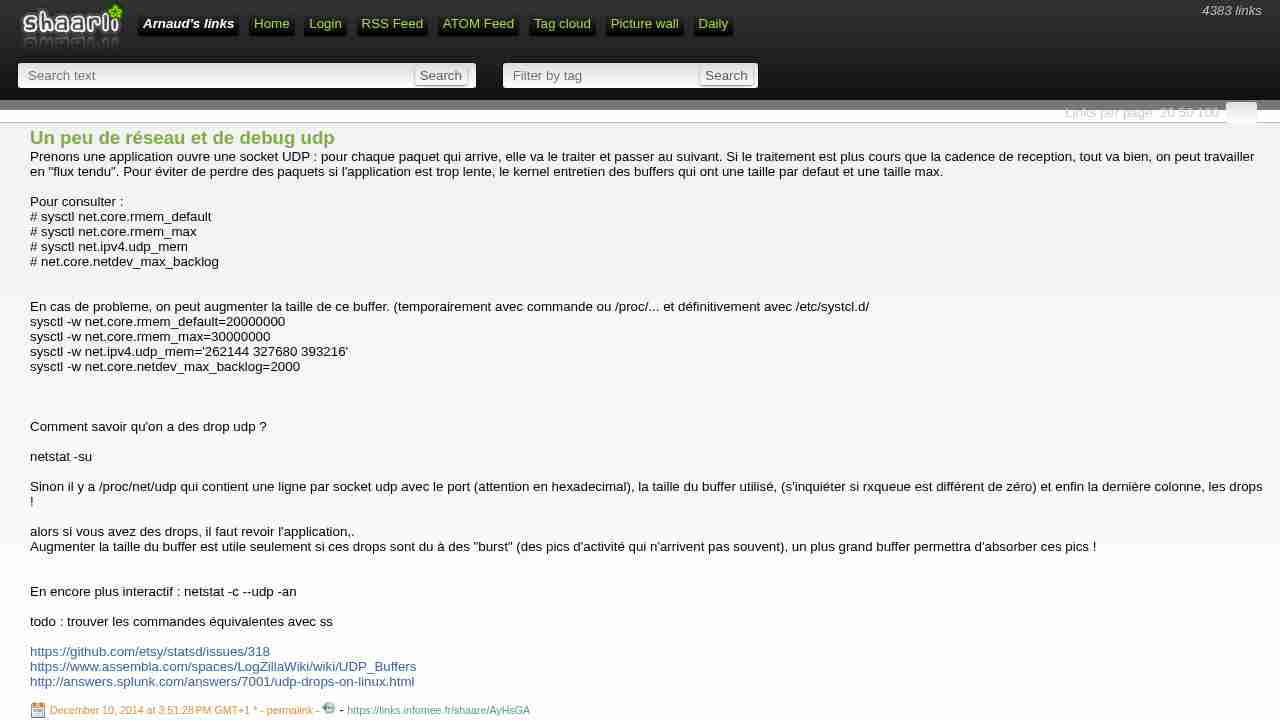
Un peu de réseau et de debug udp
December 10, 2014 - permalink - https://links.infomee.fr/shaare/AyHsGAPrenons une application ouvre une socket UDP : pour chaque paquet qui arrive, elle va le traiter et passer au suivant. Si le traitement est plus cours que la cadence de reception, tout va bien, on peut travailler en "flux tendu". Pour éviter de perdre des paquets si l'application est trop lente, le kernel entretien des buffers qui ont une taille par defaut et une taille max.
Pour consulter :
sysctl net.core.rmem_default
sysctl net.core.rmem_max
sysctl net.ipv4.udp_mem
net.core.netdev_max_backlog
En cas de probleme, on peut augmenter la taille de ce buffer. (temporairement avec commande ou /proc/... et définitivement avec /etc/systcl.d/
sysctl -w net.core.rmem_default=20000000
sysctl -w net.core.rmem_max=30000000
sysctl -w net.ipv4.udp_mem='262144 327680 393216'
sysctl -w net.core.netdev_max_backlog=2000Comment savoir qu'on a des drop udp ?
netstat -su
Sinon il y a /proc/net/udp qui contient une ligne par socket udp avec le port (attention en hexadecimal), la taille du buffer utilisé, (s'inquiéter si rxqueue est différent de zéro) et enfin la dernière colonne, les drops !
alors si vous avez des drops, il faut revoir l'application,.
Augmenter la taille du buffer est utile seulement si ces drops sont du à des "burst" (des pics d'activité qui n'arrivent pas souvent), un plus grand buffer permettra d'absorber ces pics !En encore plus interactif : netstat -c --udp -an
todo : trouver les commandes équivalentes avec ss
https://github.com/etsy/statsd/issues/318
https://www.assembla.com/spaces/LogZillaWiki/wiki/UDP_Buffers
http://answers.splunk.com/answers/7001/udp-drops-on-linux.html
-
-