-
Example 2: Bucket Owner Granting Cross-Account Bucket Permissions - Amazon Simple Storage Service
June 12, 2017 - permalink - http://docs.aws.amazon.com/AmazonS3/latest/dev/example-walkthroughs-managing-access-example2.htmlDonc pour autoriser un compte externe, on va créer une bucket policy sur notre bucket pour autoriser "arn:aws:iam::account_id:root" ou plus précis sur l'user arn:aws:iam::account_id:user/foobar ou le role
C'est le compte en face qui va décider qui a le droit de venir sur notre bucket avec des user policy standard (quand on est dans le contexte du compte en face, c'est comme si le bucket nous appartenait)
Exemple bucket policy à mettre sur le BUCKET de l'account A pour autoriser l'account xxx en RW
{
"Version": "2012-10-17",
"Statement": [{ "Sid": "Allow account_xx on aws account xxx RW", "Effect": "Allow", "Principal": { "AWS": "arn:aws:iam::OTHER_ACCOUNT_ID:root" }, "Action": ["s3:GetBucketLocation", "s3:ListBucket"], "Resource": "arn:aws:s3:::BUCKET" }, { "Sid": "Allow account_xx on aws account xxx RW", "Effect": "Allow", "Principal": { "AWS": "arn:aws:iam::OTHER_ACCOUNT_ID:root" }, "Action": [ "s3:*" ], "Resource": "arn:aws:s3:::BUCKET/*" } ]}
Pour Read only, remplacer action du deuxieme bloc par "Action": ["s3:Get","s3:List"],
-
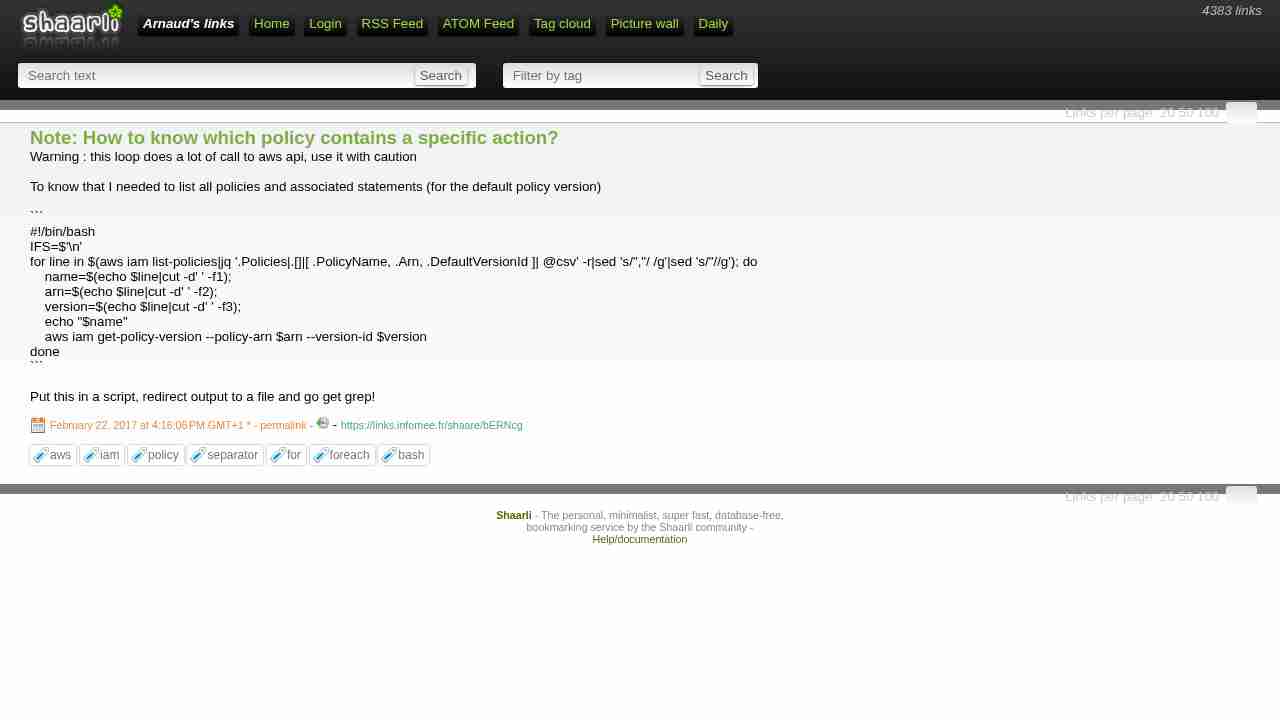
Note: How to know which policy contains a specific action?
February 22, 2017 - permalink - https://links.infomee.fr/shaare/bERNcgWarning : this loop does a lot of call to aws api, use it with caution
To know that I needed to list all policies and associated statements (for the default policy version)
#!/bin/bash
IFS=$'\n'
for line in $(aws iam list-policies|jq '.Policies|.[]|[ .PolicyName, .Arn, .DefaultVersionId ]| @csv' -r|sed 's/","/ /g'|sed 's/"//g'); do
    name=$(echo $line|cut -d' ' -f1);
    arn=$(echo $line|cut -d' ' -f2);
    version=$(echo $line|cut -d' ' -f3);
    echo "$name"
    aws iam get-policy-version --policy-arn $arn --version-id $version
done
Put this in a script, redirect output to a file and go get grep!