-
Annotations - AWS Load Balancer Controller
September 6, 2025 - permalink - https://kubernetes-sigs.github.io/aws-load-balancer-controller/v2.13/guide/ingress/annotations/#health-check[Summary, full note in Shaarli]
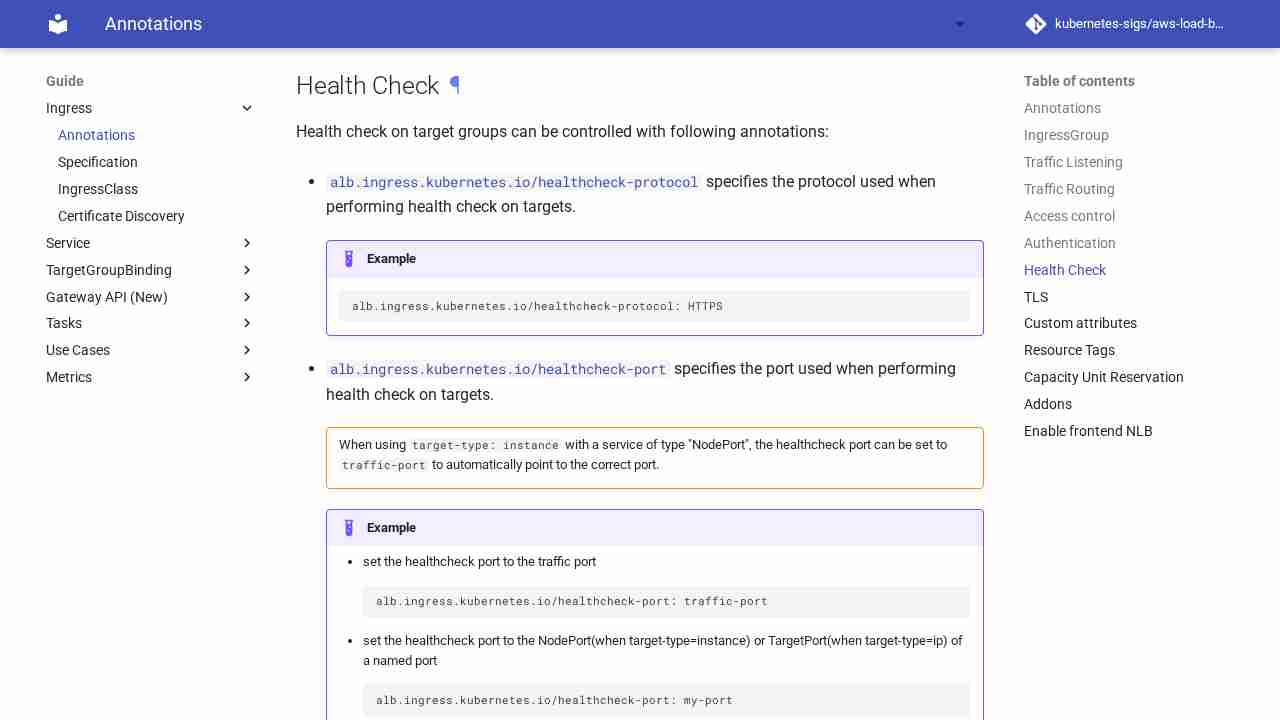
AWS Load Balancer Controller: condensed Ingress annotations (prefix alb.ingress.kubernetes.io/). Health check params: https://registry.terraform.io/providers/hashicorp/aws/latest/docs/resources/lb_target_group#health_check- Group: group.name: my-group ; group.order: -1000..1000, default 0
- Listen: listen-ports: '[{"HTTP": 80}, {"HTTPS": 443}]' ; ssl-redirect: '443' (set on one Ingress, applies to the whole group)
- Routing: load-balancer-name ; target-type: ip ; backend-protocol: HTTP|HTTPS ; backend-protocol-version: HTTP1|GRPC|HTTP2 ; subnets: names work (subnet-name-a, ...)
- Access: scheme: internal|internet-facing ; security-groups: SG names work (otherwise one SG is created)
- OIDC auth: auth-type: oidc ; auth-idp-oidc: '{"issuer","authorizationEndpoint","tokenEndpoint","userInfoEndpoint","secretName"}' ; auth-on-unauthenticated-request: authenticate ; auth-session-timeout: '86400' ; auth-session-cookie
- Health check: healthcheck-protocol: HTTP ; healthcheck-path: /ping ; healthcheck-interval-seconds 5-300 (default 30) ; healthcheck-timeout-seconds 2-120 (default 6) ; healthy- / unhealthy-threshold-count 2-10 (default 3)
- TLS: certificate-arn (can be auto-discovered from the host)
- Attributes: load-balancer-attributes: access_logs.s3.enabled=true,access_logs.s3.bucket=...,access_logs.s3.prefix=... ; routing.http2.enabled=true
Pattern: one "main" Ingress (ingressClassName alb) carries the group, listen, routing, access, health check and TLS annotations; each service's "child" Ingress only sets group.name (+ group.order) and its rules (host, path /*, service port).
-
-
-
Django ALLOWED_HOSTS for Amazon ELB - Stack Overflow
June 10, 2020 - permalink - https://stackoverflow.com/questions/35858040/django-allowed-hosts-for-amazon-elbAnother simple solution would be to write a custom MIDDLEWARE which will give the response to ELB before the ALLOWED_HOSTS is checked. So now you don't have to load ALLOWED_HOSTS dynamically.
The middleware can be as simple as:
project/app/middleware.py
from django.http import HttpResponse
from django.utils.deprecation import MiddlewareMixinclass HealthCheckMiddleware(MiddlewareMixin):
def process_request(self, request):
if request.META["PATH_INFO"] == "/ping/":
return HttpResponse("pong")settings.py
MIDDLEWARE = [
'corsheaders.middleware.CorsMiddleware',
'app.middleware.HealthCheckMiddleware',
'django.middleware.security.SecurityMiddleware',
'django.contrib.sessions.middleware.SessionMiddleware',
'django.middleware.common.CommonMiddleware',
'django.middleware.csrf.CsrfViewMiddleware',
...
]Django Middleware reference https://docs.djangoproject.com/en/dev/topics/http/middleware/